Run Bug Bounty with less noise and fair pricing

Bugbop is a bug bounty platform. Bug hunters test your app and report vulnerabilities to you. You only pay when someone finds a real bug. Our AI filters out the junk, and your own AI agent can check what's left against your code.

bugbop.com
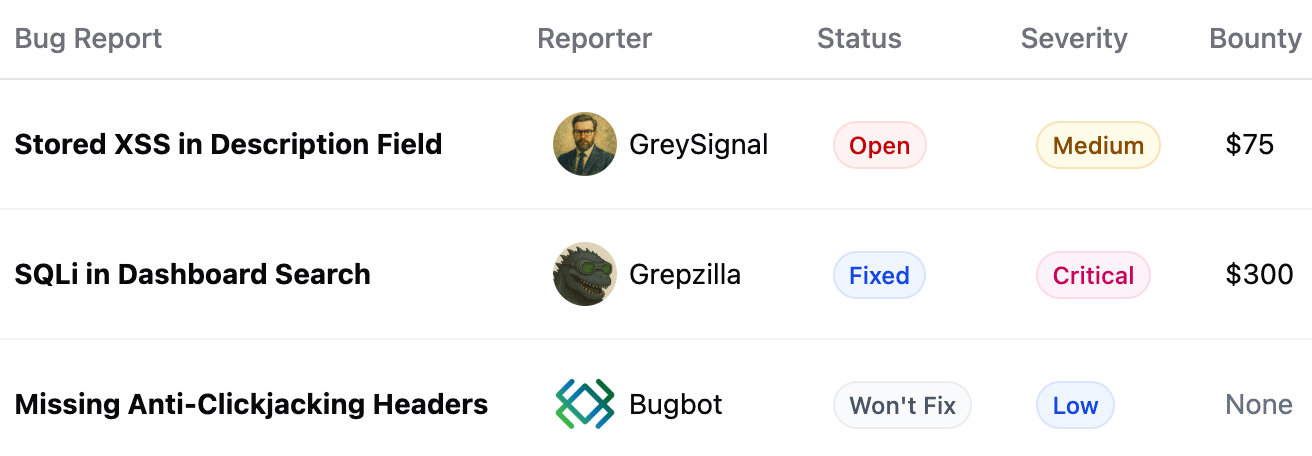
Screenshot of Bugbop UI showing some security bugs

How Bug Bounty works

Set up a program, get bugs reported, fix them, pay for the valid ones.

Create a Program

Use our templates to define what's in scope and what you'll pay. Takes a few minutes.

Invite Bug Hunters

Invite bug hunters directly or list your program publicly on Bugbop.

Bug Hunters Find Bugs

Bug hunters test your app ethically and submit bug reports through Bugbop.

AI Triage

AI pre-submission scope check. On submission, AI assigns severity and flags duplicates before your team sees anything. Your team, your own AI agent or your MSP handles final review.

Reward

Reward bug hunters for valid findings. Cash, swag, or kudos. Pay them well and they keep looking.

Fix Bugs

Prioritise and ship fixes. Your app gets more secure with every closed report.

Why bother with Bug Bounty?

Pentests are a point-in-time snapshot. Bug bounty gives you ongoing coverage from people who are motivated to actually find real bugs.

Find Bugs Before Attackers Do

Bug hunters report vulnerabilities to you instead of exploiting them. You fix the issue before it becomes an incident.

Pay for Bugs, Not Hours

No retainers, no day rates, no minimum spend. You pay a bounty when someone finds a real vulnerability. No bug, no cost.

Continuous, Not One-Off

Bug hunters keep testing as your app changes. New features, new attack surface, new bugs found.

Show You Take Security Seriously

Running a bug bounty program signals to customers and partners that you actively invest in finding and fixing vulnerabilities.

Fast Turnaround

Researchers often find critical issues within days of a program launching. When you update your program scope, bug hunters get notified and start immediately.

Compliance and Standards

Bug bounty programs support requirements for GDPR, SOC 2, ISO 27001, and other frameworks that expect ongoing vulnerability management.

Why Choose Bugbop?

Fair pricing, less noise, and you can be up and running today.

AI Pre-Submission Checks

Bug reports get checked against your scope & guidelines before they hit your team. The AI decides the initial severity and checks for duplicates.

Read more →

No Bug, No Fee

Other platforms charge $10,000s/year upfront. Bugbop has no monthly charges, no lock-in contracts, and no "contact us" pricing. You only pay fees on valid bugs.

Read more →

Fair Bounty Fees

The industry norm of 20% fees on bounties is simply price gouging. Our fees are only 15% which means more bounties are recorded in-platform too.

Read more →

Set Up in Minutes

Sign up, use our scope template, set your bounties, and go. You can start small (limited scope, low bounties) and tweak it later.

Read more →

Automated "Beg Bounties"

Tired of emails about missing CSP headers? Turn on our scanners, they raise them for you and you close them once. Next time someone reports the same thing, the AI flags it as a duplicate.

Read more →

Works With Your Agent

A REST API and an agent skill for Claude Code, Codex and Cursor on every program, at no extra charge. Paid plans add signed webhooks for n8n or your own code.

Read more →

Run It From Your Own AI Agent

Every program comes with a REST API and an open-source agent skill for Claude Code, Codex and Cursor. Your agent already has your code, logs and MCP tools, so it can tell which bugs are real almost as soon as they land.

Real or Not, in Minutes

Your agent checks each report against your code, logs and tools like Sentry. You know which bugs are real before you've read them.

Finds the Duplicates

It compares new reports with earlier ones, your open issues and your git history. Dupes and already-fixed bugs get caught straight away.

Replies in Your Voice

It drafts replies to hunters the way you write them. You approve each one before it's sent.

Tickets Without Copy-Paste

It opens Linear, Jira or GitHub issues with the report linked. One request covers every open high and critical.

Access Requests and Junk

Approve hunters with paid bounties and no strikes. Block the ones who keep sending out-of-scope reports.

You Stay in Charge

Nothing reaches a hunter without your yes, and paying a bounty stays in the browser. Start with a read-only token.

Read more →

# Install once, then add a token from your Bugbop profile

> /plugin marketplace add PonnyPtyLtd/bugbop-skills

> /plugin install bugbop@bugbop-skills

> What came in on Bugbop this week, and which of it is real?

⏺ Bash(bugbop.py GET "/reports?status=new")

⎿ 3 new reports on Acme

⏺ Read(app/controllers/invoices_controller.rb)

⏺ Bash(curl localhost:3000/api/invoices/8812 as a second test account)

⎿ 200, returns the other account's invoice

⏺ sentry - search_issues("/api/invoices")

⎿ Nothing unusual in the last 30 days

⏺ Bash(git log -S "X-Frame-Options")

⎿ Fixed in a1c93e0 on 12 March

⏺ IDOR on /api/invoices/:id is real. InvoicesController#show skips the account check and it reproduces locally, so I'd call it high.

Missing X-Frame-Options duplicates the scanner's report, fixed in March.

Self-XSS in profile bio is out of scope.

> Draft replies the way I usually write them.

⏺ IDOR: "Nice find, confirmed. Fix goes out today and we'll sort the bounty once it's live."

Header: "Thanks, this one was raised by our scanner and fixed back in March."

Self-XSS: "Self-XSS is out of scope for us, sorry. Closing as N/A."

Post these and open a Linear issue for the IDOR?

> yes

⏺ Posted 3 comments. Created ENG-412 "IDOR on /api/invoices/:id".
Not sure where to start?

Book a call and we'll walk you through setting up a program that makes sense for your app and budget.